Managed IT for law, accounting and advisory firms
We run Microsoft 365, practice and document platforms and access to client and matter files, and keep current the security evidence your insurer asks for each year.
$Managed IT cost calculator
IT for client-confidential work
Law firms, accounting practices and advisory firms hold information their clients trust them with, and each works with it differently: matters and document control, client files and lodgements, or engagements shared with clients and other advisers. We run the IT around each, from boutique partnerships to multi-office firms.
Law firms
Matters · Documents · ConfidentialityLaw firms run on matters, deadlines, document control and client confidentiality, with practice and document platforms such as LEAP, Actionstep, FilePro, iManage or NetDocuments alongside Microsoft 365.
We look after the access, email, devices and secure sharing around those platforms, with matter-level permissions and the evidence your insurer asks for.
- Matter-level access and permission control
- Reliable access to LEAP, Actionstep, FilePro or your practice system
- iManage, NetDocuments, SharePoint or hybrid document environments
- Secure email and file sharing with clients
- DLP and sensitivity labels on matter files and correspondence
- Cyber insurance evidence aligned to Essential Eight
- Copilot and AI tools set up inside matter permissions
Accounting practices
Client files · Lodgements · WorkflowAccounting practices run on client files, working papers, lodgements and recurring client work, with Xero, MYOB, BGL, Karbon and document platforms such as FYI Docs in daily use.
We look after the Microsoft 365, identity, devices and backup around those platforms.
- Reliable access to Xero, MYOB, BGL, Karbon and other practice platforms
- FYI Docs, SharePoint and OneDrive structured around clients
- myID, RAM and ATO Online services access set up and secured for every agent
- Email security against impersonation and lookalike domains
- Backups with tested restores for client files, email and practice data
- AML/CTF records kept for seven years where you provide a designated service
- Onboarding, offboarding and extra support capacity for tax season
Advisory firms
Engagements · Deliverables · DeadlinesAdvisory firms work across consulting, corporate finance, risk, restructuring and commercial advice, with deliverables, board papers and client workspaces moving between teams and clients.
We set up Teams and SharePoint around engagements, control collaboration with clients, and keep AI tools inside the firm’s data boundaries.
- Teams and SharePoint structured around clients and engagements
- Controlled collaboration with clients and other advisers
- Copilot and AI tools inside firm-controlled systems
- Privileged access, MFA and endpoint security
- Backups with tested restores for deliverables, email and project records
- Power BI and reporting access set up with the right permissions
- Cyber insurance evidence and Essential Eight-aligned controls
Evidence your insurer and clients can rely on
Insurers, larger clients and auditors now ask firms to show their controls. We keep that evidence current in your support portal and the monthly reporting you already receive, so renewal questionnaires and client security reviews are answered from records.
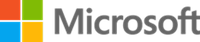
The same groundwork comes before Copilot: permissions reviewed, labels applied and old sharing links removed before AI reaches client files.
- 1MFA on every accountCoverage report from Entra ID, with exceptions listedMonthly
- 2Privileged accessAdmin accounts reviewed and kept separateQuarterly
- 3Patching and endpoint protectionPatch level and EDR coverage for every deviceMonthly
- 4Backups and restore testsImmutable copies, with restore results recordedQuarterly
- 5Email securitySPF, DKIM and DMARC, with impersonation protectionMonthly
- 1Permissions reviewSharePoint, Teams and OneDrive access checked client by clientBefore rollout
- 2Sharing links“Anyone” links and stale guest access removedBefore rollout
- 3Sensitivity labelsClient, tax and matter documents labelledBefore rollout
- 4DLP policiesClient data checked before it leaves by email or TeamsOngoing
- 5Approved tools and loggingAI tools, data boundaries and audit logs agreedMonthly
The systems we look after day to day
The IT we look after around your practice platforms, client files and deadlines.
Users and IT support
Partners, fee earners and support staff message us in Microsoft Teams and follow the request there, with AI-assisted triage routing it to the right engineer. When a deadline is at risk, it’s a P1. Under our SLA-driven support model, the response target for a P1 incident is under 15 minutes.
Microsoft 365 and identity
MFA, Conditional Access and role-based permissions on every account, with access set up and removed as fee earners, graduates and contractors join, move or leave. Data loss prevention (DLP) and sensitivity labels are part of the setup, covering client files, matter documents and correspondence.
Computers and devices
Office and remote laptops, home-office setups and phones are managed to one standard, with endpoint protection, encryption and patching scheduled outside business hours.
Cloud, infrastructure and networks
Microsoft 365, Azure and hybrid document environments, chosen for how the firm’s files and practice platforms behave. Secure remote access, Wi-Fi and links between offices let people work from the office, from home or at a client’s premises.
Backup and recovery
Immutable backups across Microsoft 365, email, document platforms, client files and practice data, with restores tested. Systems are restored in the order client work needs them, starting with sign-in, email and live matters or engagements.
Vendors and practice platforms
LEAP, Actionstep, iManage, NetDocuments, Xero, MYOB, FYI Docs and NetSuite all depend on the devices, sign-in and connectivity we manage, and we coordinate with each vendor.
Cybersecurity and client data
Identity, endpoint and email security, patching and privileged access are part of the service, with Essential Eight-aligned controls and SOC and MDR where client data or your insurer calls for it. We watch mailbox rules and risky sign-ins for signs of business email compromise.
Copilot, AI and automation
Permissions, labels and old sharing links are cleaned up before Copilot reaches client files. We also agree rules for approved AI tools and build automation with Power Automate for document requests, client onboarding and reporting, inside the firm’s data boundaries.
See the outcomes we’ve delivered for our clients
Questions we get asked
Do the AML/CTF reforms affect our firm?
Do you support LEAP, Actionstep, iManage or NetDocuments?
Do you support Xero, MYOB, QuickBooks or FYI Docs?
What cyber insurance evidence do insurers ask professional firms for?
Is it safe to use Copilot with client files?
How do we protect the firm against business email compromise?
Do the new Privacy Act rules on automated decisions affect our firm?
What happens to access when a fee earner or contractor leaves?
Can you work alongside our internal IT or operations manager?
What reporting and reviews do we get?
How much does Managed IT cost for a professional firm?
How does onboarding work for a firm?
Do you help with myID and ATO Online services for agents?
Explore the services we provide
We run the firm’s day-to-day IT.
LEAP · Xero · iManage · FYI Docs environmentsExplore Managed IT →We protect client data with controls you can evidence.
Essential Eight alignment · cyber insurance evidenceExplore Cybersecurity →We give the firm secure access from the office, home and client sites.
Fortinet and Cisco Meraki capabilityExplore Networks & SD-WAN →We run the platforms that hold client and matter data.
Azure · Microsoft 365 · hybrid document environmentsExplore Infrastructure & Cloud →We set up Copilot and AI tools and put them to work.
Copilot deployment · Power Platform · governed AIExplore AI & Automation →We source and deploy the hardware and licences your firm runs on.
Laptops · scanners · practice-software licensingExplore Technology Procurement →Protect client data and put AI to work safely
Tell us how your firm works today, and we’ll identify where security, backup and AI tools like Copilot can be improved.
Discuss Managed ITCalculate Managed IT costPrefer email? contact@inlightit.com.au